

After passed my ISO-IEC-27005-Risk-Manager exam with your help, I am planning to take other examination and I am sure I can pass it with Prep4sureGuide too!
 Hale


The ISO-IEC-27005-Risk-Manager exam has a reputation for catching even experienced professionals off guard. Prep4sureGuide prepares you with 62 practice questions that match the style and depth of the PECB Certified ISO/IEC 27005 Risk Manager exam, refreshed for 2026.
| Certification Vendor: | PECB |
|---|---|
| Exam Name: | PECB Certified ISO/IEC 27005 Risk Manager Exam |
| Exam Number: | ISO-IEC-27005-Risk-Manager |
| Real Exam Qty: | 60 |
| Exam Price: | $300 - $450 USD |
| Certificate Validity Period: | 3 years |
| Exam Duration: | 120 minutes |
| Exam Format: | Multiple-choice questions, Scenario-based questions |
| Passing Score: | 70% |
| Available Languages: | French, Portuguese, Spanish, Italian, German, English |
| Related Certifications: | PECB Certified ISO/IEC 27005 Lead Risk Manager PECB Certified ISO/IEC 27005 Provisional Risk Manager |
| Recommended Training: | PECB ISO/IEC 27005 Risk Manager Training Course |
| Exam Registration: | PECB Official Registration |
| Sample Questions: |  |
| Exam Way: | Online proctored or onsite at authorized exam centers |
| Pre Condition: | Basic knowledge of information security and ISO/IEC 27001; no mandatory prior certification required; for full certification: 2 years professional experience including 1 year in risk management, 200 hours of relevant activities, sign PECB Code of Ethics |
| Official Syllabus URL: | https://pecb.com/en/education-and-certification-for-individuals/iso-iec-27005/iso-iec-27005-risk-manager |
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Fundamental Principles and Concepts of Information Security Risk Management | 25% | - Risk management concepts and definitions
|
| Topic 2: Implementation of an Information Security Risk Management Program | 25% | - Program design and planning
|
| Topic 3: Information Security Risk Management Framework and Processes | 30% | - Processes per ISO/IEC 27005
|
| Topic 4: Other Information Security Risk Assessment Methodologies | 20% | - Common assessment methods
|
The ISO-IEC-27005-Risk-Manager exam is the official exam behind the PECB Certified ISO/IEC 27005 Risk Manager credential from PECB. It sits at the Manager level of the PECB certification track. It is also associated with PECB Certified ISO/IEC 27005 Provisional Risk Manager, PECB Certified ISO/IEC 27005 Lead Risk Manager. The Prep4sureGuide practice questions on this page map to the same objectives, so you can measure your readiness before you book a seat.
The ISO-IEC-27005-Risk-Manager exam contains 60 questions and gives you 120 minutes to complete them. That pace leaves little room for getting stuck, so train yourself to flag a hard question, move on, and circle back later. Run at least one full timed session in the Prep4sureGuide test engine a week before your exam date to check whether your pacing holds under pressure.
You need 70% to pass the ISO-IEC-27005-Risk-Manager exam, and the official registration fee is $300 - $450 USD. A retake means paying that fee again in full, which makes thorough preparation the cheaper option by far. Before scheduling, take a timed Prep4sureGuide practice test; if you are not scoring comfortably above the passing line, give yourself more study time instead of booking on hope.
Basic knowledge of information security and ISO/IEC 27001; no mandatory prior certification required; for full certification: 2 years professional experience including 1 year in risk management, 200 hours of relevant activities, sign PECB Code of Ethics
Requirements can change, so confirm the latest details on the official PECB exam page before you register.
You can book the ISO-IEC-27005-Risk-Manager exam through the following official channels:
The exam is delivered Online proctored or onsite at authorized exam centers, so pick the option that suits you when booking.
PECB points candidates to these official courses:
Once you have worked through the official material, wrap up your preparation with the 62 practice questions from Prep4sureGuide to lock in what you have learned.
Yes. A free ISO-IEC-27005-Risk-Manager PDF demo is available, so you can check the question style and answer quality before you commit. Every purchase also includes 365 days of free updates, and if your product expires after that, you can extend the update service at a 50% discount from your member zone.
Your purchase is protected by our 100% Money Back Guarantee. If you take the ISO-IEC-27005-Risk-Manager exam within 60 days of purchase and do not pass, send us a scanned enrollment slip and your official Score Report PDF within two days of the exam; approved refunds are processed within seven days. The candidate name must match the payer name, and the guarantee does not apply to exams taken within three days of purchase, to products that were downloaded but never used in an exam sitting, or to free materials and expired orders. If you would rather keep studying, we can instead exchange your order for two free exam products of equal value while your original product keeps its update service. Delivery itself is instant: your download is emailed within one minute of payment and stays available in your member zone, with no limit on how many computers you can install it on. If nothing arrives within two hours, contact our customer service team.
The ISO-IEC-27005-Risk-Manager syllabus is divided into 4 domains, including Implementation of an Information Security Risk Management Program (25%), Other Information Security Risk Assessment Methodologies (20%), and Fundamental Principles and Concepts of Information Security Risk Management (25%). The complete breakdown, with every domain and its subtopics, is listed in the Exam Topics section above — review it line by line and flag the areas where you feel weakest.
Scenario 1
The risk assessment process was led by Henry, Bontton's risk manager. The first step that Henry took was identifying the company's assets. Afterward, Henry created various potential incident scenarios. One of the main concerns regarding the use of the application was the possibility of being targeted by cyber attackers, as a great number of organizations were experiencing cyberattacks during that time. After analyzing the identified risks, Henry evaluated them and concluded that new controls must be implemented if the company wants to use the application. Among others, he stated that training should be provided to personnel regarding the use of the application and that awareness sessions should be conducted regarding the importance of protecting customers' personal data.
Lastly, Henry communicated the risk assessment results to the top management. They decided that the application will be used only after treating the identified risks.
Based on the scenario above, answer the following question:
Bontton established a risk management process based on ISO/IEC 27005, to systematically manage information security threats. Is this a good practice?
Correct Answer: A 🗳️
Explanation: Only visible for Prep4sureGuide members. You can sign-up / login (it's free).
Scenario 6: Productscape is a market research company headquartered in Brussels, Belgium. It helps organizations understand the needs and expectations of their customers and identify new business opportunities. Productscape's teams have extensive experience in marketing and business strategy and work with some of the best-known organizations in Europe. The industry in which Productscape operates requires effective risk management. Considering that Productscape has access to clients' confidential information, it is responsible for ensuring its security. As such, the company conducts regular risk assessments. The top management appointed Alex as the risk manager, who is responsible for monitoring the risk management process and treating information security risks.
The last risk assessment conducted was focused on information assets. The purpose of this risk assessment was to identify information security risks, understand their level, and take appropriate action to treat them in order to ensure the security of their systems. Alex established a team of three members to perform the risk assessment activities. Each team member was responsible for specific departments included in the risk assessment scope. The risk assessment provided valuable information to identify, understand, and mitigate the risks that Productscape faces.
Initially, the team identified potential risks based on the risk identification results. Prior to analyzing the identified risks, the risk acceptance criteria were established. The criteria for accepting the risks were determined based on Productscape's objectives, operations, and technology. The team created various risk scenarios and determined the likelihood of occurrence as "low," "medium," or "high." They decided that if the likelihood of occurrence for a risk scenario is determined as "low," no further action would be taken. On the other hand, if the likelihood of occurrence for a risk scenario is determined as "high" or "medium," additional controls will be implemented. Some information security risk scenarios defined by Productscape's team were as follows:
1. A cyber attacker exploits a security misconfiguration vulnerability of Productscape's website to launch an attack, which, in turn, could make the website unavailable to users.
2. A cyber attacker gains access to confidential information of clients and may threaten to make the information publicly available unless a ransom is paid.
3. An internal employee clicks on a link embedded in an email that redirects them to an unsecured website, installing a malware on the device.
The likelihood of occurrence for the first risk scenario was determined as "medium." One of the main reasons that such a risk could occur was the usage of default accounts and password. Attackers could exploit this vulnerability and launch a brute-force attack. Therefore, Productscape decided to start using an automated "build and deploy" process which would test the software on deploy and minimize the likelihood of such an incident from happening. However, the team made it clear that the implementation of this process would not eliminate the risk completely and that there was still a low possibility for this risk to occur. Productscape documented the remaining risk and decided to monitor it for changes.
The likelihood of occurrence for the second risk scenario was determined as "medium." Productscape decided to contract an IT company that would provide technical assistance and monitor the company's systems and networks in order to prevent such incidents from happening.
The likelihood of occurrence for the third risk scenario was determined as "high." Thus, Productscape decided to include phishing as a topic on their information security training sessions. In addition, Alex reviewed the controls of Annex A of ISO/IEC 27001 in order to determine the necessary controls for treating this risk. Alex decided to implement control A.8.23 Web filtering which would help the company to reduce the risk of accessing unsecure websites. Although security controls were implemented to treat the risk, the level of the residual risk still did not meet the risk acceptance criteria defined in the beginning of the risk assessment process. Since the cost of implementing additional controls was too high for the company, Productscape decided to accept the residual risk. Therefore, risk owners were assigned the responsibility of managing the residual risk.
Based on scenario 6, Alex reviewed the controls of Annex A of ISO/IEC 27001 to determine the necessary controls for treating the risk described in the third risk scenario. According to the guidelines of ISO/IEC 27005, is this acceptable?
Correct Answer: C 🗳️
Explanation: Only visible for Prep4sureGuide members. You can sign-up / login (it's free).
Scenario 4: In 2017, seeing that millions of people turned to online shopping, Ed and James Cordon founded the online marketplace for footwear called Poshoe. In the past, purchasing pre-owned designer shoes online was not a pleasant experience because of unattractive pictures and an inability to ascertain the products' authenticity. However, after Poshoe's establishment, each product was well advertised and certified as authentic before being offered to clients. This increased the customers' confidence and trust in Poshoe's products and services. Poshoe has approximately four million users and its mission is to dominate the second-hand sneaker market and become a multi-billion dollar company.
Due to the significant increase of daily online buyers, Poshoe's top management decided to adopt a big data analytics tool that could help the company effectively handle, store, and analyze dat a. Before initiating the implementation process, they decided to conduct a risk assessment. Initially, the company identified its assets, threats, and vulnerabilities associated with its information systems. In terms of assets, the company identified the information that was vital to the achievement of the organization's mission and objectives. During this phase, the company also detected a rootkit in their software, through which an attacker could remotely access Poshoe's systems and acquire sensitive data.
The company discovered that the rootkit had been installed by an attacker who had gained administrator access. As a result, the attacker was able to obtain the customers' personal data after they purchased a product from Poshoe. Luckily, the company was able to execute some scans from the target device and gain greater visibility into their software's settings in order to identify the vulnerability of the system.
The company initially used the qualitative risk analysis technique to assess the consequences and the likelihood and to determine the level of risk. The company defined the likelihood of risk as "a few times in two years with the probability of 1 to 3 times per year." Later, it was decided that they would use a quantitative risk analysis methodology since it would provide additional information on this major risk. Lastly, the top management decided to treat the risk immediately as it could expose the company to other issues. In addition, it was communicated to their employees that they should update, secure, and back up Poshoe's software in order to protect customers' personal information and prevent unauthorized access from attackers.
According to scenario 4, Poshoe has identified its assets, vulnerabilities, and threats associated with its information systems. What does the company need in order to start identifying its existing controls?
Correct Answer: C 🗳️
Explanation: Only visible for Prep4sureGuide members. You can sign-up / login (it's free).
Scenario 8: Biotide is a pharmaceutical company that produces medication for treating different kinds of diseases. The company was founded in 1997, and since then it has contributed in solving some of the most challenging healthcare issues.
As a pharmaceutical company, Biotide operates in an environment associated with complex risks. As such, the company focuses on risk management strategies that ensure the effective management of risks to develop high-quality medication. With the large amount of sensitive information generated from the company, managing information security risks is certainly an important part of the overall risk management process. Biotide utilizes a publicly available methodology for conducting risk assessment related to information assets. This methodology helps Biotide to perform risk assessment by taking into account its objectives and mission. Following this method, the risk management process is organized into four activity areas, each of them involving a set of activities, as provided below.
1. Activity area 1: The organization determines the criteria against which the effects of a risk occurring can be evaluated. In addition, the impacts of risks are also defined.
2. Activity area 2: The purpose of the second activity area is to create information asset profiles. The organization identifies critical information assets, their owners, as well as the security requirements for those assets. After determining the security requirements, the organization prioritizes them. In addition, the organization identifies the systems that store, transmit, or process information.
3. Activity area 3: The organization identifies the areas of concern which initiates the risk identification process. In addition, the organization analyzes and determines the probability of the occurrence of possible threat scenarios.
4. Activity area 4: The organization identifies and evaluates the risks. In addition, the criteria specified in activity area 1 is reviewed and the consequences of the areas of concerns are evaluated. Lastly, the level of identified risks is determined.
The table below provides an example of how Biotide assesses the risks related to its information assets following this methodology:
Based on the scenario above, answer the following question: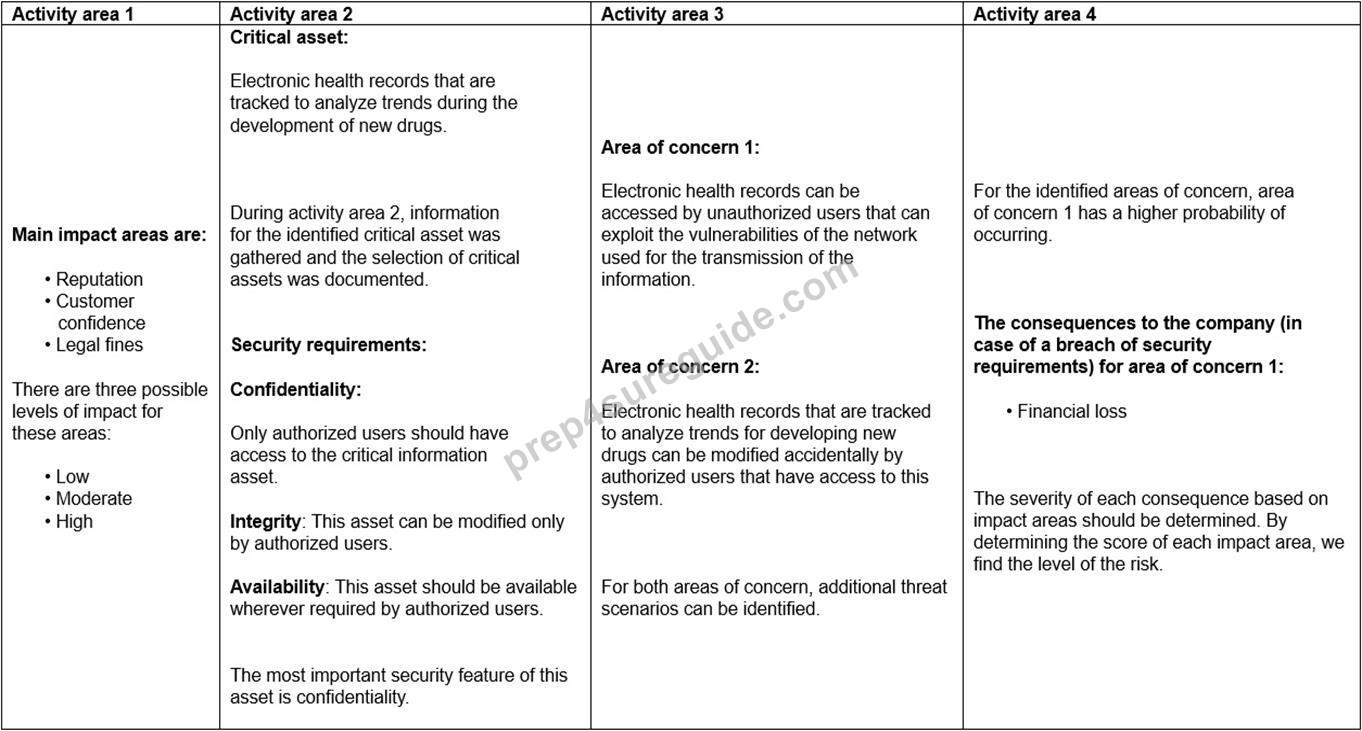
Which risk assessment methodology does Biotide use?
Correct Answer: B 🗳️
Explanation: Only visible for Prep4sureGuide members. You can sign-up / login (it's free).
Scenario 3: Printary is an American company that offers digital printing services. Creating cost-effective and creative products, the company has been part of the printing industry for more than 30 years. Three years ago, the company started to operate online, providing greater flexibility for its clients. Through the website, clients could find information about all services offered by Printary and order personalized products. However, operating online increased the risk of cyber threats, consequently, impacting the business functions of the company. Thus, along with the decision of creating an online business, the company focused on managing information security risks. Their risk management program was established based on ISO/IEC 27005 guidelines and industry best practices.
Last year, the company considered the integration of an online payment system on its website in order to provide more flexibility and transparency to customers. Printary analyzed various available solutions and selected Pay0, a payment processing solution that allows any company to easily collect payments on their website. Before making the decision, Printary conducted a risk assessment to identify and analyze information security risks associated with the software. The risk assessment process involved three phases: identification, analysis, and evaluation. During risk identification, the company inspected assets, threats, and vulnerabilities. In addition, to identify the information security risks, Printary used a list of the identified events that could negatively affect the achievement of information security objectives. The risk identification phase highlighted two main threats associated with the online payment system: error in use and data corruption After conducting a gap analysis, the company concluded that the existing security controls were sufficient to mitigate the threat of data corruption. However, the user interface of the payment solution was complicated, which could increase the risk associated with user errors, and, as a result, impact data integrity and confidentiality.
Subsequently, the risk identification results were analyzed. The company conducted risk analysis in order to understand the nature of the identified risks. They decided to use a quantitative risk analysis methodology because it would provide more detailed information. The selected risk analysis methodology was consistent with the risk evaluation criteri a. Firstly, they used a list of potential incident scenarios to assess their potential impact. In addition, the likelihood of incident scenarios was defined and assessed. Finally, the level of risk was defined as low.
In the end, the level of risk was compared to the risk evaluation and acceptance criteria and was prioritized accordingly.
Based on the scenario above, answer the following question:
What type of risk identification approach did Printary use?
Correct Answer: B 🗳️
Explanation: Only visible for Prep4sureGuide members. You can sign-up / login (it's free).
Viewing page 1 out of 13 pages.
Viewing questions 1-5 out of 62 questions.

Over 37234+ Satisfied Customers
After passed my ISO-IEC-27005-Risk-Manager exam with your help, I am planning to take other examination and I am sure I can pass it with Prep4sureGuide too!
Hale
You can trust this ISO-IEC-27005-Risk-Manager study material, the Q&A are all the latest and valid. It is so good to pass the exam. Thank you!
 Lydia
There are two different languages to buy the ISO-IEC-27005-Risk-Manager exam questions, i may chose the wrong one if i didn't ask for the service, they are so kind and professional. I passed the exam today and i think you will feel happy for me as well.
 Adonis

My company asks me to get the ISO-IEC-27005-Risk-Manager certification asap. When I was felt worried, I found this ISO-IEC-27005-Risk-Manager study guide, it is very helpful. Yeah, I am happy to say I passed my exam now.
 Vic
Hey guys, i have taken the ISO-IEC-27005-Risk-Manager test recently and passed, so i recommended this exam dump to use and hope you can pass it quickly.
 Malcolm
These ISO-IEC-27005-Risk-Manager exam dumps are very valid. I passed my ISO-IEC-27005-Risk-Manager exam after using them for practice.
 Amy

I will, you guys have always been really good whenever I buy stuff from u and need ISO/IEC 27005 questions answering.
 Clifford
The ISO-IEC-27005-Risk-Manager exam dump really covered all details with relevant practical questions. And i have passed the exam only deponding on it. It didn't let me down. Great!
 Bruce
The price for ISO-IEC-27005-Risk-Manager study guide was reasonable, and I can afford it. Besides, I bought PDF and Online and Soft version, and there was a preferential price for purchasing three versions, pretty good.
 Raymond
Passed today with god grace. The dump is valid for 94% of the questions. Worth going through the this dumps thoroughly before you take the exams to make sure you pass! All the best!
 Murphy
My friends passed ISO-IEC-27005-Risk-Manager exam with your dumps pdf, so i want to have a try with your dumps, wish me a good luck.
 Maud
I bought the amazing Prep4sureGuide ISO-IEC-27005-Risk-Manager dumps a week before my exam. I had no mind that they would help me and I would pass exam.
 Victoria
Passed the ISO-IEC-27005-Risk-Manager exam today with the ISO-IEC-27005-Risk-Manager study guide. This has really helped me to clarify all my doubts regarding the exam topics. Also, the answered questions are great help. So, I can surely recommend it to all exam candidates.
 Abel
Thank you for the great ISO-IEC-27005-Risk-Manager study guides.
 Jamie
These ISO-IEC-27005-Risk-Manager exam questions are the latest you should have and they are accurate. I took the exam in the last day of this month, and i passed with a high score out of my expection. Thanks!
 Letitia
When i was sitting for the ISO-IEC-27005-Risk-Manager exam, i was confident for i had used the ISO-IEC-27005-Risk-Manager learning questions to prapare, and i passed the exam smoothly as they predicted. Wonderful exam materials!
 Earl
Prep4sureGuide really handy for me and I prepared my exam within few days, I passed my ISO-IEC-27005-Risk-Manager exam with good marks. Great value!
 Morton
It was entirely different from the classroom training.
 Nick
I cant beleive i just hit it, it was a wonderful opportunity and testing my skills was an awesome experience, just loved it .
 Jay
The ISO-IEC-27005-Risk-Manager exam dumps in Prep4sureGuide are quite well and i passed my exam on 12/8/2018. Wonderful!
 Harvey
Prep4sureGuide Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
If you prepare for the exams using our Prep4sureGuide testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
Prep4sureGuide offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.


Our sure prep material equipped with the highest experts team and the most authoritative exam items plus the best service, which can ensure you 100% pass. Besides, our exam training guide can support both the fastest delivery speed and the shortest time to get all knowledge.
Copyright © 2026 Prep4sureGuide NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy
