


The Best FCSS_CDS_AR-7.6 Exam Study Material and Preparation Test Question Dumps
Get Ready to Pass the FCSS_CDS_AR-7.6 exam Right Now Using Our Fortinet Certified Solution Specialist Exam Package
Fortinet FCSS_CDS_AR-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 41
The DevOps team is troubleshooting a FortiGate software-defined network(SDN) connector that is failing to integrate with a Kubernetes cluster. While using several debug commands, they find that the connector connection generates an error code 401.
What is the cause of this error?
Response:
- A. The Kubernetes cluster is using an unsupported API version.
- B. The configured client secret credentials are incorrect.
- C. The service principal being used has the correct role assigned.
- D. The FortiGate firewall is using HTTP to send API calls instead of HTTPS.
Answer: B
NEW QUESTION # 42
You are automating configuration changes on one of the FortiGate VMs using Linux Red Hat Ansible.
How does Linux Red Hat Ansible connect to FortiGate to make the configuration change?
- A. It uses a YAML file.
- B. It uses an API.
- C. It uses SSH.
- D. It uses a FortiGate VIP.
Answer: B
Explanation:
Ansible connects to FortiGate through APIs (REST API/HTTPS) when using Fortinet Ansible modules. The YAML playbook defines the tasks, but the actual configuration changes are pushed via the FortiGate API.
NEW QUESTION # 43
What is the main advantage of using SD-WAN Transit Gateway Connect over traditional SD-WAN?
- A. You can use BGP over IPsec for maximum throughput.
- B. You can combine it with IPsec to achieve higher bandwidth.
- C. It eliminates the use of ECMP.
- D. You can use GRE-based tunnel attachments.
Answer: D
NEW QUESTION # 44
An Azure administration team is looking for a FortiGate high availability (HA) solution that is able to:
- Filter east-west traffic
- Filter north-south traffic
- Scale up
- Scale out
Which HA deployment meets all of the requirements?
- A. Active-active with external and internal load balancers
- B. Active-passive with SDN connector
- C. Active-passive with external and internal load balancers
- D. Active-active with Azure Gateway load balancer
Answer: A
NEW QUESTION # 45
Which AWS monitoring service provides comprehensive observability for applications and infrastructure?
Response:
- A. AWS Auto Scaling
- B. AWS Shield
- C. AWS Config
- D. Amazon CloudWatch
Answer: D
NEW QUESTION # 46
In the context of Fortinet's integration with cloud-native tools, what does the term "cloud-native" refer to?
Response:
- A. Virtual machines running in data centers
- B. Applications developed for on-premises deployment
- C. Legacy applications migrated to the cloud
- D. Tools and services built to operate within cloud environments
Answer: D
NEW QUESTION # 47
A DevOps team is configuring Terraform to deploy Amazon Web Services (AWS) resources. They want to use environment variables to authenticate Terraform with AWS, while ensuring that the setup works across multiple developers' machines without exposing credentials in configuration files.
Which two environment variables must the team configure, at a minimum, to allow Terraform to authenticate with AWS?
(Choose two.)
Response:
- A. AWS_ROLE_ARN
- B. AWS_ACCESS_KEY_ID
- C. AWS_SECRET_ACCESS_KEY
- D. AWS_ACCOUNT_ID
Answer: B,C
NEW QUESTION # 48
An Azure administration team is looking for a FortiGate high availability (HA) solution that is able to:
- Filter east-west traffic
- Filter north-south traffic
- Scale up
- Scale out
Which HA deployment meets all of the requirements?
Response:
- A. Active-active with external and internal load balancers
- B. Active-passive with SDN connector
- C. Active-passive with external and internal load balancers
- D. Active-active with Azure Gateway load balancer
Answer: A
NEW QUESTION # 49
Your organization has several FortiGate VMs deployed in Azure. You need to implement a solution with Azure native tools that allows you to determine whether packets are being permitted or blocked by the FortiGate VMs.
Which solution can you use to meet these requirements?
- A. Insert the VM traffic logs in Azure Sentinel.
- B. Configure Azure Advisor to analyze the network traffic.
- C. Install the Azure Monitor agent in all VMs.
- D. Use IP flow verify for each of the VMs.
Answer: D
Explanation:
Azure IP flow verify is part of Network Watcher and lets you check if traffic is allowed or denied for a specific VM by analyzing its effective security rules and routing. This provides visibility into whether packets are being permitted or blocked for the FortiGate VMs.
NEW QUESTION # 50
Which statement about Transit Gateway (TGW) in Amazon Web Services (AWS) is true?
- A. Both the TGW attachment and propagation must be in the same TGW route table.
- B. A TGW attachment can be associated with multiple TGW route tables.
- C. TGW can have multiple TGW route tables.
- D. The TGW default route table cannot be disabled.
Answer: C
Explanation:
In AWS, a Transit Gateway (TGW) can indeed have multiple TGW route tables, allowing flexible routing policies for different VPCs and VPN attachments. Each attachment can be associated with only one route table, but TGW supports multiple route tables for segmentation and control.
NEW QUESTION # 51
Which Terraform commands help troubleshoot AWS networking resources?
(Choose two.)
Response:
- A. terraform debug
- B. terraform plan
- C. terraform apply
- D. terraform graph
Answer: B,D
NEW QUESTION # 52
Which AWS service provides real-time monitoring for firewall traffic logs?
Response:
- A. AWS WAF
- B. AWS CloudTrail
- C. AWS Network Firewall
- D. AWS Firewall Manager
Answer: C
NEW QUESTION # 53
Refer to the exhibit. An administrator used the what-if tool to preview changes to an Azure Bicep file. What will happen if the administrator decides to apply these changes in Azure?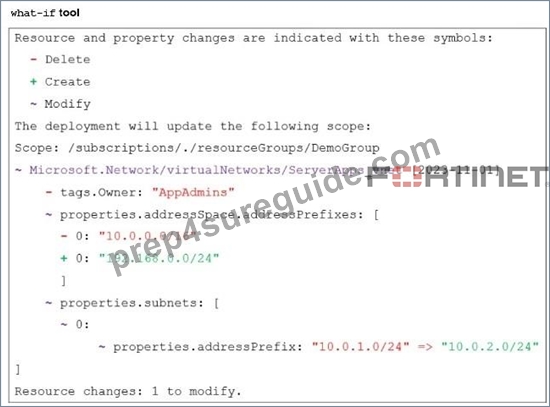
- A. This deployment will fail and no changes will be applied.
- B. Subnet 10.0.1.0/24 will replace subnet 10.0.2.0/24.
- C. A new subnet will be added to ServerApps.
- D. The ServerApps VNet will be renamed.
Answer: C
Explanation:
The what-if output shows that the ServerApps VNet will be modified:
* A new address prefix 192.168.0.0/24 will be added.
* An existing subnet will be modified from 10.0.1.0/24 to 10.0.2.0/24.
Since these are additive and modification changes within the VNet, the result is that a new subnet will be added alongside the update to the existing subnet.
NEW QUESTION # 54
Refer to the exhibit.
Refer to the exhibit.
In your Amazon Web Services (AWS), you must allow inbound HTTPS access to the Customer VPC FortiGate VM from the internet. However, your HTTPS connection to the FortiGate VM in the Customer VPC is not successful.
Also, you must ensure that the Customer VPC FortiGate VM sends all the outbound internet traffic through the Security VPC.
How do you correct this issue with minimal configuration changes? (Choose three.)
- A. Deploy an internet gateway, associate an EIP with the Customer VPC private subnet, and then add a new route with destination 0.0.0.0/0 with the internet gateway as the target.
- B. Add a route with your local internet public IP address as the destination and the internet gateway as the target.
- C. Add a route with your local internet public IP address as the destination and the transit gateway as the target.
- D. Add a route to the destination 0.0.0.0/0 with the transit gateway as the target.
- E. Deploy an internet gateway, attach it to the Customer VPC, and then associate an EIP with port1 of the FortiGate in the Customer VPC.
Answer: C,D,E
NEW QUESTION # 55
An administrator is configuring a software-defined network (SDN) connector in FortiWeb to dynamically obtain information about existing objects in an Amazon Elastic Kubernetes Service (EKS) cluster.
Which AWS policy should the administrator attach to a user to achieve this goal?
- A. AmazonEKSServicePolicy
- B. AmazonEKSClusterPolicy
- C. AmazonEKSConnectorServiceRolePolicy
- D. AmazonEKSComputePolicy
Answer: B
NEW QUESTION # 56
Which of the following AWS services can be used for monitoring cloud security and compliance?
(Choose two.)
Response:
- A. AWS CodeDeploy
- B. AWS Config
- C. AWS Lambda
- D. AWS Security Hub
Answer: B,D
NEW QUESTION # 57
Which AWS service can simulate network paths to troubleshoot connectivity issues?
(Choose two.)
Response:
- A. AWS Reachability Analyzer
- B. AWS CloudTrail
- C. AWS Network Manager
- D. AWS Config
Answer: A,C
NEW QUESTION # 58
Refer to the exhibit. You are troubleshooting a FortiGate HA floating IP issue with Microsoft Azure. After the failover, the new primary device does not have the previous primary device floating IP address.
What could be the possible issue with this scenario?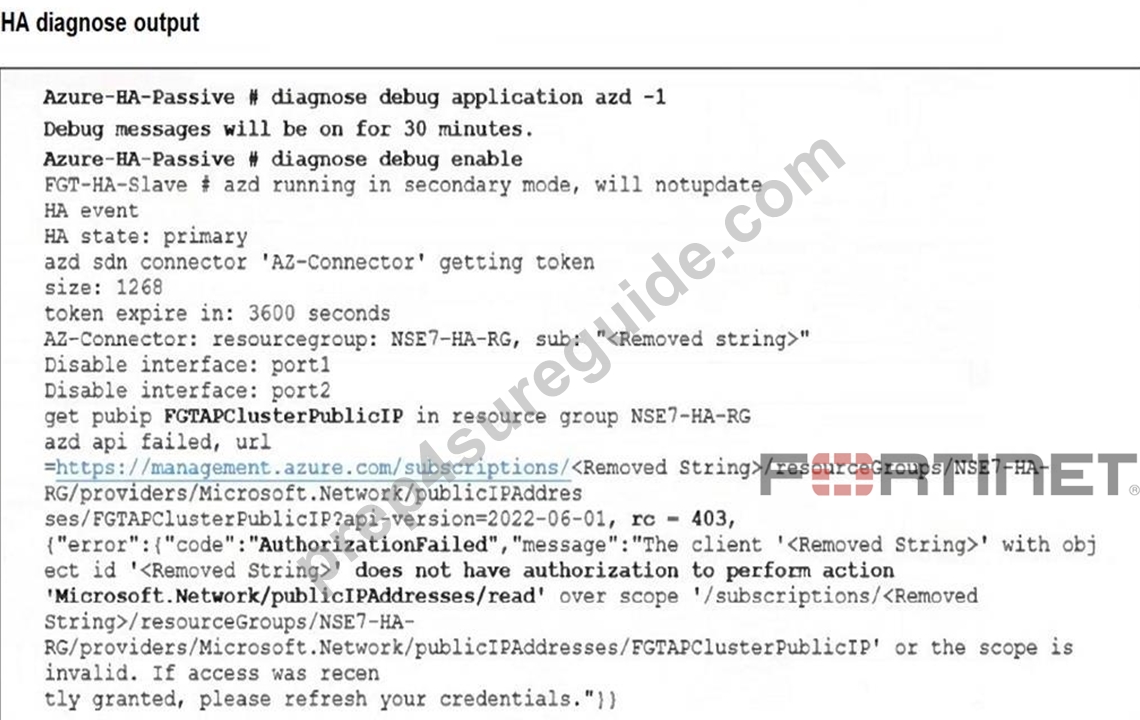
- A. A wrong client secret credential is used.
- B. FortiGate port4 does not have internet access.
- C. The Azure service principal account must have a contributor role.
- D. The error is caused by credential time expiration.
Answer: C
Explanation:
The debug output shows an AuthorizationFailed (403) error when FortiGate tries to update the Azure public IP. This indicates the Azure service principal account used by FortiGate does not have sufficient permissions. To manage floating IPs in HA, the service principal must be assigned at least the Contributor role on the subscription or resource group.
NEW QUESTION # 59
Refer to the exhibit. You are tasked to deploy a FortiGate VM with private and public subnets in Amazon Web Services (AWS). You examined the variables.tffile. Assume that all the other terraform files are in place.
What will be the final result after running the terraform initand terraform apply commands?
- A. Terraform will deploy a FortiGate VM in the eu-West-1a availability zone without any subnets.
- B. Terraform will not deploy a FortiGate VM.
- C. Terraform will deploy a FortiGate VM in the eu-West-1a availability zone with two subnets and BYOL license.
- D. Terraform will deploy a FortiGate VM in the eu-West-1 region with private and public subnets.
Answer: C
Explanation:
The variables.tf file specifies:
- Region: eu-west-1
- Availability zone: eu-west-1a
- Two subnets (publiccidraz1 = 10.1.0.0/24 and privatecidraz1 = 10.1.1.0/24)
- License type: byol
After running terraform init and terraform apply, Terraform provisions a FortiGate VM in eu-west-
1a with both a public and private subnet using a BYOL license.
NEW QUESTION # 60
Refer to the exhibit. In which type of FortiCNP insights can an administrator examine the findings triggered by this policy?
- A. Data
- B. Threat
- C. User activity
- D. Risk
Answer: B
Explanation:
The policy shown is an AV Scan Policy that scans for malware during discovery and raises alerts when malicious targets are accessed. Findings from such policies are categorized under Threat insights in FortiCNP, since they deal with detection of malware and malicious activity.
NEW QUESTION # 61
Refer to the exhibit. You deployed a FortiGate HA active-passive cluster in Microsoft Azure.
Which two statements regarding this particular deployment are true? (Choose two.)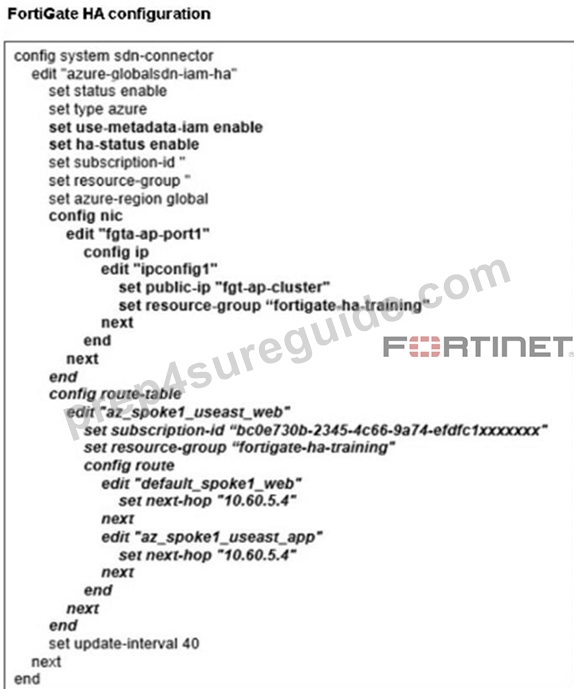
- A. There is no SLA for API calls from Microsoft Azure.
- B. You can use the vim-exception command to synchronize the configuration.
- C. The configuration does not synchronize between the primary and secondary devices.
- D. During a failover, all existing sessions are transferred to the new active FortiGate.
Answer: A,B
Explanation:
In Azure HA for FortiGate, failover relies on Azure API calls to update routing and public IP associations. Microsoft does not provide an SLA for these API calls, which can affect failover timing.
FortiGate HA in Azure supports configuration synchronization, but you can exclude specific VDOMs from syncing using the vdom-exception command.
NEW QUESTION # 62
Refer to the exhibit.
An experienced AWS administrator is creating a new virtual public cloud (VPC) flow log with the settings shown in the exhibit. What is the purpose of this configuration? Response:
- A. To monitor the logs in real time
- B. To store the logs for further analysis
- C. To troubleshoot a log flow issue
- D. To maximize the number of logs saved
Answer: B
NEW QUESTION # 63
......
Get Special Discount Offer of FCSS_CDS_AR-7.6 Certification Exam Sample Questions and Answers: https://www.prep4sureguide.com/FCSS_CDS_AR-7.6-prep4sure-exam-guide.html
Enhance Your Career With Available Preparation Guide for FCSS_CDS_AR-7.6 Exam: https://drive.google.com/open?id=1e3dK_WpTk8QOP7WAlHH5b1RxvxFbN2cV