


Jan-2023 Get Totally Free Updates on 350-201 Dumps PDF Questions
Prepare With Top Rated High-quality 350-201 Dumps For Success in 350-201 Exam
NEW QUESTION 76
Refer to the exhibit.
Where are the browser page rendering permissions displayed?
- A. x-test-debug
- B. x-xss-protection
- C. x-content-type-options
- D. x-frame-options
Answer: C
NEW QUESTION 77
Refer to the exhibit.
An engineer is analyzing this Vlan0386-int12-117.pcap file in Wireshark after detecting a suspicious network activity. The origin header for the direct IP connections in the packets was initiated by a google chrome extension on a WebSocket protocol. The engineer checked message payloads to determine what information was being sent off-site but the payloads are obfuscated and unreadable. What does this STIX indicate?
- A. The extension is not performing as intended because of restrictions since ports 80 and 443 should be accessible
- B. There is a possible data leak because payloads should be encoded as UTF-8 text
- C. The traffic is legitimate as the google chrome extension is reaching out to check for updates and fetches this information
- D. There is a malware that is communicating via encrypted channels to the command and control server
Answer: B
NEW QUESTION 78 
Refer to the exhibit. An engineer configured this SOAR solution workflow to identify account theft threats and privilege escalation, evaluate risk, and respond by resolving the threat. This solution is handling more threats than Security analysts have time to analyze. Without this analysis, the team cannot be proactive and anticipate attacks. Which action will accomplish this goal?
- A. Exclude the step "BAN malicious IP" to allow analysts to conduct and track the remediation
- B. Include a step "Take a Snapshot" to capture the endpoint state to contain the threat for analysis
- C. Include a step "Reporting" to alert the security department of threats identified by the SOAR reporting engine
- D. Exclude the step "Check for GeoIP location" to allow analysts to analyze the location and the associated risk based on asset criticality
Answer: A
NEW QUESTION 79
Drag and drop the type of attacks from the left onto the cyber kill chain stages at which the attacks are seen on the right.
Answer:
Explanation:
NEW QUESTION 80 
Refer to the exhibit. An engineer received a report that an attacker has compromised a workstation and gained access to sensitive customer data from the network using insecure protocols. Which action prevents this type of attack in the future?
- A. Use syslog to gather data from multiple sources and detect intrusion logs for timely responses
- B. Deploy a SOAR solution and correlate log alerts from customer zones
- C. Use VLANs to segregate zones and the firewall to allow only required services and secured protocols
- D. Deploy IDS within sensitive areas and continuously update signatures
Answer: C
NEW QUESTION 81
A SIEM tool fires an alert about a VPN connection attempt from an unusual location. The incident response team validates that an attacker has installed a remote access tool on a user's laptop while traveling. The attacker has the user's credentials and is attempting to connect to the network.
What is the next step in handling the incident?
- A. Block the source IP from the firewall
- B. Identify lateral movement
- C. Identify systems or services at risk
- D. Perform an antivirus scan on the laptop
Answer: C
NEW QUESTION 82
Refer to the exhibit.
An engineer is performing static analysis of a file received and reported by a user. Which risk is indicated in this STIX?
- A. The file is redirecting users to a website that requests privilege escalations from the user.
- B. The file is redirecting users to a website that is determining users' geographic location.
- C. The file is redirecting users to a website that harvests cookies and stored account information.
- D. The file is redirecting users to the website that is downloading ransomware to encrypt files.
Answer: B
NEW QUESTION 83
Refer to the exhibit.
What results from this script?
- A. Domains are compared to seed rules
- B. A list of domains as seeds is blocked
- C. Seeds for existing domains are checked
- D. A search is conducted for additional seeds
Answer: D
NEW QUESTION 84
An engineer notices that unauthorized software was installed on the network and discovers that it was installed by a dormant user account. The engineer suspects an escalation of privilege attack and responds to the incident. Drag and drop the activities from the left into the order for the response on the right.
Answer:
Explanation:
NEW QUESTION 85
According to GDPR, what should be done with data to ensure its confidentiality, integrity, and availability?
- A. Conduct a data protection impact assessment
- B. Conduct penetration testing
- C. Perform awareness testing
- D. Perform a vulnerability assessment
Answer: A
NEW QUESTION 86 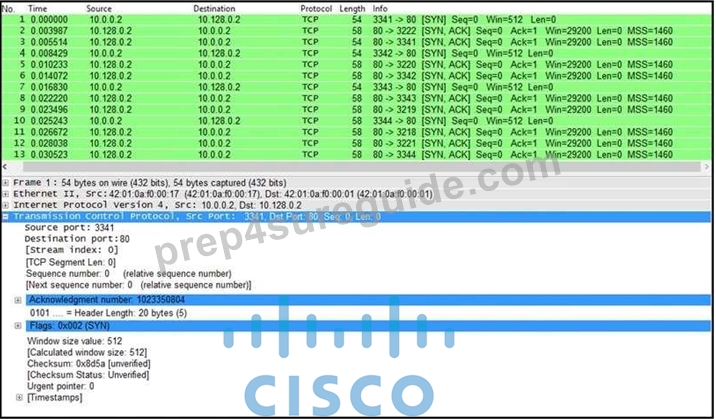
Refer to the exhibit. What is the threat in this Wireshark traffic capture?
- A. A high rate of SYN packets being sent from a single source IP toward multiple destination IPs
- B. A high rate of SYN packets being sent from multiple sources toward a single destination IP
- C. A flood of ACK packets coming from a single source IP to multiple destination IPs
- D. A flood of SYN packets coming from a single source IP to a single destination IP
Answer: D
NEW QUESTION 87
Refer to the exhibit.
The Cisco Secure Network Analytics (Stealthwatch) console alerted with "New Malware Server Discovered" and the IOC indicates communication from an end-user desktop to a Zeus C&C Server. Drag and drop the actions that the analyst should take from the left into the order on the right to investigate and remediate this IOC.
Answer:
Explanation:
NEW QUESTION 88
Drag and drop the function on the left onto the mechanism on the right.
Answer:
Explanation:
NEW QUESTION 89
An organization had an incident with the network availability during which devices unexpectedly malfunctioned. An engineer is investigating the incident and found that the memory pool buffer usage reached a peak before the malfunction. Which action should the engineer take to prevent this issue from reoccurring?
- A. Enable memory tracing notifications.
- B. Enable memory threshold notifications.
- C. Disable CPU threshold trap toward the SNMP server.
- D. Disable memory limit.
Answer: B
NEW QUESTION 90 
Refer to the exhibit. An engineer is reverse engineering a suspicious file by examining its resources. What does this file indicate?
- A. an archived malware
- B. a Windows executable file
- C. a MS-DOS executable archive
- D. a DOS MZ executable format
Answer: B
Explanation:
Explanation/Reference: https://stackoverflow.com/questions/2577545/why-is-this-program-cannot-be-run-in-dos-mode-text- present-in-dll-files#:~:text=The%20linker%20places%20a%20default,using%20the%20%2FSTUB%20linker%
20option.&text=This%20information%20enables%20Windows%20to,has%20an%20MS-DOS%20stub.
NEW QUESTION 91
......
Get 100% Success with Latest CyberOps Professional 350-201 Exam Dumps: https://www.prep4sureguide.com/350-201-prep4sure-exam-guide.html
350-201 Free Certification Exam Easy to Download PDF Format 2023: https://drive.google.com/open?id=1w37RwkaXcfYav8wYjWrBbrs-ucc4nlej