


[UPDATED 2026] Getting 200-201 Certification Made Easy!
200-201 Exam Crack Test Engine Dumps Training With 478 Questions
Cisco 200-201 certification exam is designed to test candidates' knowledge and skills in the field of cybersecurity operations. It is a fundamental level certification that covers the basics of cybersecurity operations and the associated technologies, tools, and procedures. 200-201 exam is intended for professionals who are interested in starting or advancing their careers in the cybersecurity field.
Cisco 200-201 exam consists of 100 questions that candidates must complete within 120 minutes. 200-201 exam fee is $300, and it is available in English and Japanese. Candidates who pass the exam will earn the Cisco Certified CyberOps Associate certification, which demonstrates their ability to identify and remediate cybersecurity threats, and work effectively in a SOC environment. Understanding Cisco Cybersecurity Operations Fundamentals certification is a valuable asset for individuals who want to start their career in cybersecurity and for those who want to advance their skills in this field.
NEW QUESTION # 263
Which type of evidence supports a theory or an assumption that results from initial evidence?
- A. indirect
- B. probabilistic
- C. corroborative
- D. best
Answer: C
NEW QUESTION # 264
A network engineer discovers that a foreign government hacked one of the defense contractors in their home country and stole intellectual property. What is the threat agent in this situation?
- A. the defense contractor who stored the intellectual property
- B. the foreign government that conducted the attack
- C. the intellectual property that was stolen
- D. the method used to conduct the attack
Answer: B
NEW QUESTION # 265
Refer to the exhibit.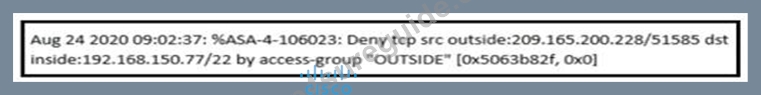
An analyst received this alert from the Cisco ASA device, and numerous activity logs were produced. How should this type of evidence be categorized?
- A. indirect
- B. best
- C. circumstantial
- D. corroborative
Answer: B
NEW QUESTION # 266
An engineer is working with the compliance teams to identify the data passing through the network. During analysis, the engineer informs the compliance team that external penmeter data flows contain records, writings, and artwork Internal segregated network flows contain the customer choices by gender, addresses, and product preferences by age. The engineer must identify protected data. Which two types of data must be identified'? (Choose two.)
- A. copyright
- B. PCI
- C. SOX
- D. PII
- E. PHI
Answer: D,E
Explanation:
Protected data refers to any information that can be used on its own or with other information to identify, contact, or locate a single person, or to identify an individual in context. In the scenario described, the engineer must identify data that is considered protected under privacy laws and regulations. Personal Identifiable Information (PII) and Protected Health Information (PHI) are two types of data that are considered protected.
PII includes any data that could potentially identify a specific individual, such as addresses and gender. PHI refers to any information about health status, provision of health care, or payment for health care that can be linked to an individual. This is what makes both PII and PHI crucial to be identified and protected in compliance with data protection regulations.
References: The Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) course provides insights into identifying protected data and the importance of safeguarding it within a network1.
NEW QUESTION # 267
Which system monitors local system operation and local network access for violations of a security policy?
- A. host-based intrusion detection
- B. antivirus
- C. systems-based sandboxing
- D. host-based firewall
Answer: A
Explanation:
Explanation
HIDS is capable of monitoring the internals of a computing system as well as the network packets on its network interfaces. Host-based firewall is a piece of software running on a single Host that can restrict incoming and outgoing Network activity for that host only.
NEW QUESTION # 268
A company encountered a breach on its web servers using IIS 7 5 Dunng the investigation, an engineer discovered that an attacker read and altered the data on a secure communication using TLS 1 2 and intercepted sensitive information by downgrading a connection to export-grade cryptography. The engineer must mitigate similar incidents in the future and ensure that clients and servers always negotiate with the most secure protocol versions and cryptographic parameters. Which action does the engineer recommend?
- A. Install the latest IIS version.
- B. Downgrade to TLS 1.1.
- C. Deploy an intrusion detection system
- D. Upgrade to TLS v1 3.
Answer: D
Explanation:
Upgrading to TLS v1.3 is recommended because it eliminates outdated cryptographic functions and reduces the risk of downgrade attacks, which can occur when attackers force connections to use weaker encryption. TLS v1.3 only supports secure cipher suites and algorithms, enhancing the security of communications.
NEW QUESTION # 269
Which principle is being followed when an analyst gathers information relevant to a security incident to determine the appropriate course of action?
- A. decision making
- B. data mining
- C. due diligence
- D. rapid response
Answer: A
NEW QUESTION # 270
Which two protocols are used for DDoS amplification attacks? (Choose two.)
- A. DNS
- B. TCP
- C. NTP
- D. ICMPv6
- E. HTTP
Answer: A,C
NEW QUESTION # 271
Refer to the exhibit.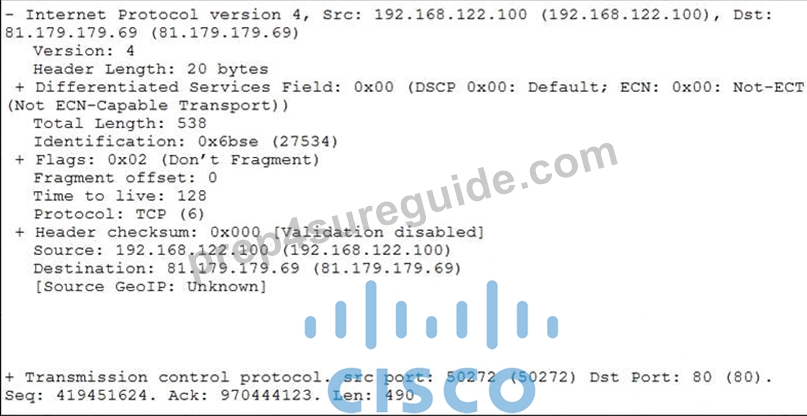
What should be interpreted from this packet capture?
- A. 81.179.179.69 is sending a packet from port 50272 to port 80 of IP address 192.168.122.100 using TCP UDP protocol.
- B. 192.168.122.100 is sending a packet from port 80 to port 50272 of IP address 81.179.179.69 using UDP protocol.
- C. 81.179.179.69 is sending a packet from port 80 to port 50272 of IP address 192.168.122.100 using UDP protocol.
- D. 192.168.122.100 is sending a packet from port 50272 to port 80 of IP address 81.179.179.69 using TCP protocol.
Answer: D
Explanation:
The packet capture exhibit shows that the source IP address is 192.168.122.100 and it is sending a packet from source port 50272 to destination port 80 of destination IP address 81.179.179.69 using TCP protocol.
The TCP protocol is indicated by the Protocol field which has the value 6. The source and destination ports are indicated by the SrcPort and DstPort fields respectively. The source and destination IP addresses are indicated by the SrcAddr and DstAddr fields respectively. References := Cisco Cybersecurity Operations Fundamentals - Module 3: Network Data and Event Analysis
NEW QUESTION # 272 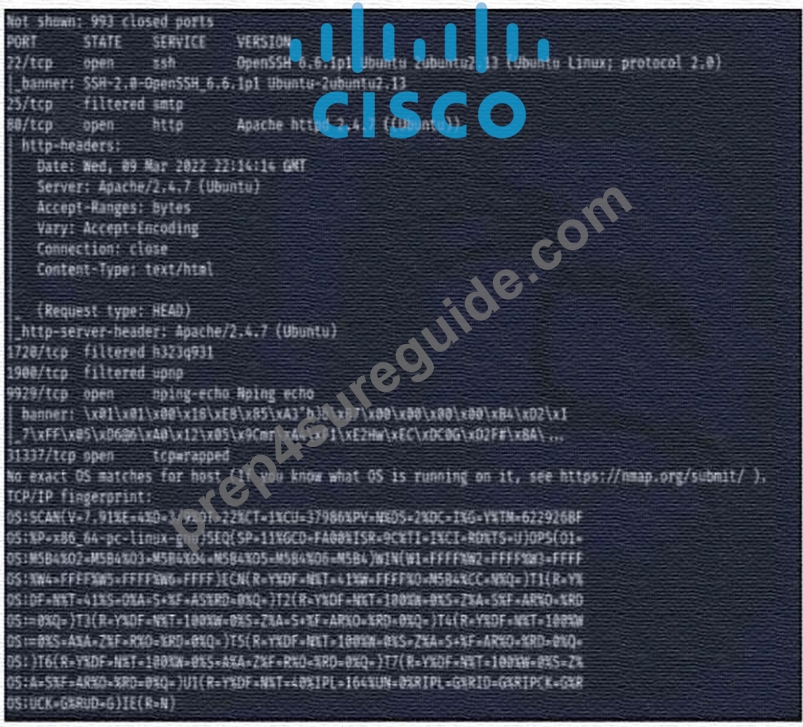
Refer to the exhibit A penetration tester runs the Nmap scan against the company server to uncover possible vulnerabilities and exploit them Which two elements can the penetration tester identity from the scan results?
(Choose two.)
- A. server purpose and functionality
- B. server uptime and internal clock
- C. UIDs and group identifiers
- D. number of concurrent connections the server can handle
- E. running services and applications
Answer: A,E
NEW QUESTION # 273
What is the difference between indicator of attack (loA) and indicators of compromise (loC)?
- A. loA is the evidence that a security breach has occurred, and loC allows organizations to act before the vulnerability can be exploited.
- B. loC is the evidence that a security breach has occurred, and loA allows organizations to act before the vulnerability can be exploited.
- C. loC refers to the individual responsible for the security breach, and loA refers to the resulting loss.
- D. loA refers to the individual responsible for the security breach, and loC refers to the resulting loss.
Answer: B
Explanation:
Indicators of Compromise (IoC) are pieces of forensic data, such as system log entries or files, that suggest an intrusion may have occurred. Indicators of Attack (IoA) are signs that an attack may be underway, allowing organizations to take action before any potential breach occurs.
References: The CBROPS course materials cover the concepts of IoC and IoA, explaining how they are used in cybersecurity operations to detect and prevent security incidents.
NEW QUESTION # 274
Drag and drop the elements from the left into the correct order for incident handling on the right.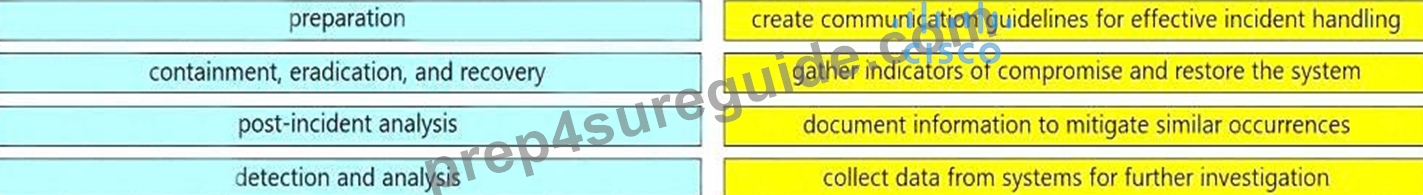
Answer:
Explanation: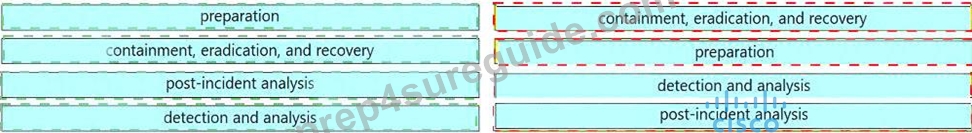
NEW QUESTION # 275
Drag and drop the definition from the left onto the phase on the right to classify intrusion events according to the Cyber Kill Chain model.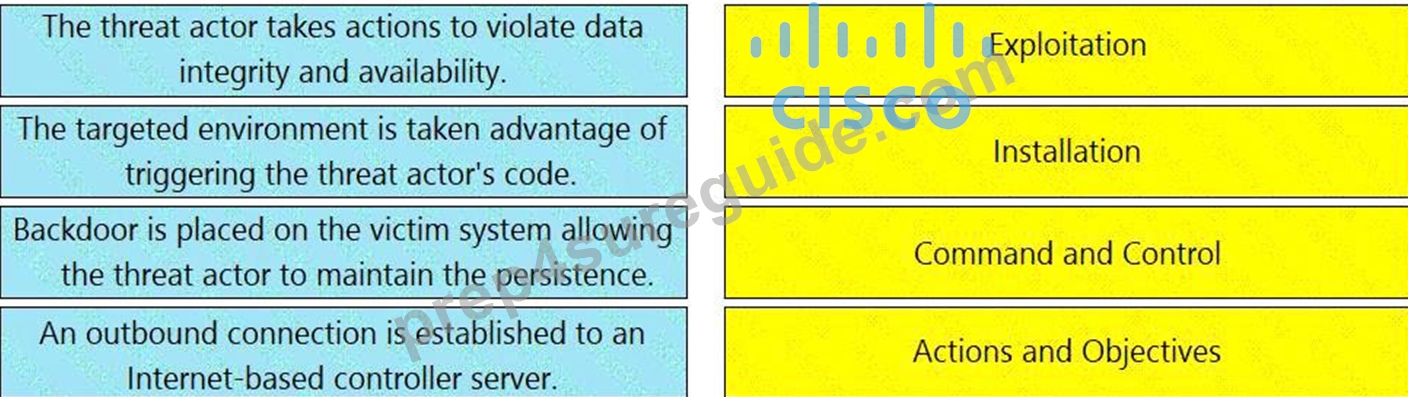
Answer:
Explanation: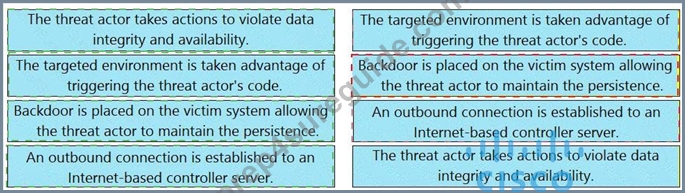
Explanation:
Exploitation - The targeted Environment is taken advantage of triggering the threat actor's code Installation - Backdoor is placed on the victim system allowing the threat actor to maintain the persistence.
Command and Control - An outbound connection is established to an Internet-based controller server.
Actions and Objectives - The threat actor takes actions to violate data integrity and availability
NEW QUESTION # 276
Drag and drop the event term from the left onto the description on the right.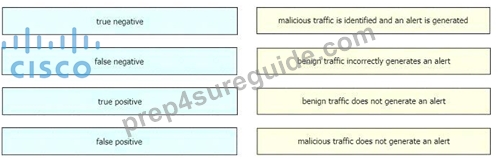
Answer:
Explanation: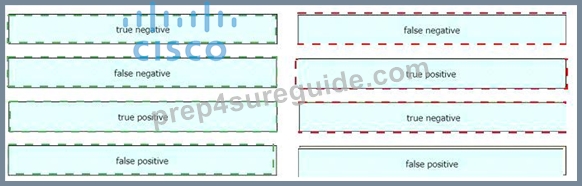
Explanation:
A screenshot of a computer Description automatically generated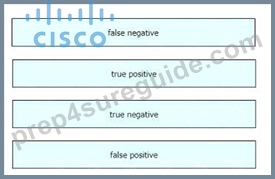
NEW QUESTION # 277
Refer to the exhibit.
Which type of evidence is this file?
- A. corroborating evidence
- B. direct evidence
- C. best evidence
- D. circumstantial evidence
Answer: A
NEW QUESTION # 278
......
200-201 Exam Dumps Contains FREE Real Quesions from the Actual Exam: https://www.prep4sureguide.com/200-201-prep4sure-exam-guide.html
Obtain the 200-201 PDF Dumps Get 100% Outcomes Exam Questions For You To Pass: https://drive.google.com/open?id=1uvoZebilxPG-8GLURyABpM_U3UHCQnBk